



Modern corporate governance and institutional operations across Enterprise Software Engineering and Lean Six Sigma Deployment require an uncompromising commitment to rigorous systems architecture, analytical depth, and proactive risk mitigation. In contemporary commercial operating environments, organizations managing Lean Six Sigma in Enterprise Tech face synchronized macroeconomic disruptions, complex regulatory enforcement mandates, and rapid technological transformations. Enterprises that rely on obsolete manual processes or fragmented departmental data architectures within Lean Six Sigma in Enterprise Tech find themselves vulnerable to severe capital impairment, unexpected operational shutdowns, and sudden statutory penalties. Developing institutional resilience in Enterprise Software Engineering and Lean Six Sigma Deployment demands embedding systematic operational protocols, verifiable compliance metrics, and automated data telemetry into core executive decision-making.
Empirical management practices demonstrate that enterprise value creation in Enterprise Software Engineering and Lean Six Sigma Deployment is fundamentally linked to the maturity of underlying operational governance. Applying DMAIC statistical control frameworks to agile continuous integration/continuous deployment (CI/CD) pipelines compresses software defects, eliminates deployment rework, and optimizes engineering cycle velocity. Progressive leadership teams construct multi-layered defensive frameworks that link risk management, capital budgeting, and operational efficiency into a unified operational fabric for Lean Six Sigma in Enterprise Tech. By methodically identifying balance-sheet vulnerabilities before broader market disruptions unfold across Enterprise Software Engineering and Lean Six Sigma Deployment, forward-thinking enterprises protect corporate profit margins, maintain superior credit ratings, and preserve decisive strategic agility.
This comprehensive publication delivers an exhaustive analytical examination of Lean Six Sigma in Enterprise Tech, deconstructing its theoretical foundations, mathematical modeling parameters, statutory compliance mandates, and practical implementation frameworks. Across 12 structured thematic sections, every critical dimension of operational execution in Enterprise Software Engineering and Lean Six Sigma Deployment is analyzed with empirical precision, providing institutional directors, corporate treasurers, operations managers, and chief technology officers with an authoritative operational blueprint designed for long-term commercial excellence.
Across competitive global ecosystems, the cost of operational negligence in Lean Six Sigma in Enterprise Tech has escalated exponentially. Regulatory fines, shareholder derivative actions, catastrophic operational standstills, and unhedged balance-sheet drawdowns within Enterprise Software Engineering and Lean Six Sigma Deployment can destroy decades of accumulated institutional brand equity within a single fiscal cycle. Establishing a disciplined, data-driven posture across Enterprise Software Engineering and Lean Six Sigma Deployment transforms compliance from an expensive administrative burden into an enduring commercial advantage, ensuring uninterrupted operational continuity and premium market valuation.
Applying DMAIC Methodologies to Software Development and IT Workflows
Establishing an institutional operating posture within Applying DMAIC Methodologies to Software Development and IT Workflows requires enterprise leadership to deconstruct systemic dependencies across modern Lean Six Sigma in Enterprise Tech networks. Detailed analytical evaluations indicate that procedural deficiencies surrounding Applying DMAIC Methodologies to Software Development and IT Workflows stem primarily from fragmented oversight mechanisms and delayed incident escalation protocols. Consequently, structuring a comprehensive operational defense around Applying DMAIC Methodologies to Software Development and IT Workflows ensures that core institutional capabilities remain unimpaired throughout prolonged periods of commercial turbulence.
From a quantitative modeling standpoint, managing Applying DMAIC Methodologies to Software Development and IT Workflows requires deploying sophisticated econometric formulas and continuous statistical variance analyses within Lean Six Sigma in Enterprise Tech. Financial controllers monitor key performance thresholds in Applying DMAIC Methodologies to Software Development and IT Workflows, mandating that operational throughput matches predefined benchmarks while defect rates remain strictly controlled. Embedding these quantitative benchmarks for Applying DMAIC Methodologies to Software Development and IT Workflows into automated financial ledgers ensures that corporate capital allocations remain disciplined, defensible, and fully aligned with strategic corporate objectives.
Deploying structured operational workflows within Applying DMAIC Methodologies to Software Development and IT Workflows requires configuring automated data telemetry and real-time monitoring across all functional Lean Six Sigma in Enterprise Tech touchpoints. For enterprise organizations seeking regulatory clarity regarding Applying DMAIC Methodologies to Software Development and IT Workflows, referencing validated benchmarks published by institutional portals such as State of DevOps continuous delivery benchmarks provides foundational compliance criteria that satisfy external regulatory authorities and institutional audit bodies. This automated operational telemetry layer for Applying DMAIC Methodologies to Software Development and IT Workflows transforms reactive troubleshooting into proactive risk containment, ensuring continuous business continuity across high-pressure environments.
From a regulatory compliance perspective, managing Applying DMAIC Methodologies to Software Development and IT Workflows requires strict adherence to statutory directives, regional licensing requirements, and industry-specific covenants governing Lean Six Sigma in Enterprise Tech. Corporate legal counsel must verify that all operational documentation regarding Applying DMAIC Methodologies to Software Development and IT Workflows strictly aligns with statutory disclosure rules, mitigating the risk of administrative penalties or statutory enforcement inquiries. This rigorous statutory posture surrounding Applying DMAIC Methodologies to Software Development and IT Workflows shields the enterprise against costly administrative proceedings, safeguarding institutional capital and protecting corporate leadership from personal liability.
Long-term institutional governance over Applying DMAIC Methodologies to Software Development and IT Workflows demands structured board oversight, unannounced third-party compliance audits, and transparent executive scorecards across Lean Six Sigma in Enterprise Tech. Comprehensive audit trails and timestamped forensic logs for Applying DMAIC Methodologies to Software Development and IT Workflows provide corporate leadership with verifiable legal evidence of proactive operational diligence, protecting executive directors against shareholder litigation. Ultimately, establishing these institutional governance protocols for Applying DMAIC Methodologies to Software Development and IT Workflows guarantees that corporate operations remain structurally sound, commercially competitive, and fully compliant with statutory expectations.
Value Stream Mapping for Slashing Digital Deployment Lead Times
Establishing an institutional operating posture within Value Stream Mapping for Slashing Digital Deployment Lead Times requires enterprise leadership to deconstruct systemic dependencies across modern Lean Six Sigma in Enterprise Tech networks. Detailed analytical evaluations indicate that procedural deficiencies surrounding Value Stream Mapping for Slashing Digital Deployment Lead Times stem primarily from fragmented oversight mechanisms and delayed incident escalation protocols. Consequently, structuring a comprehensive operational defense around Value Stream Mapping for Slashing Digital Deployment Lead Times ensures that core institutional capabilities remain unimpaired throughout prolonged periods of commercial turbulence.
From a quantitative modeling standpoint, managing Value Stream Mapping for Slashing Digital Deployment Lead Times requires deploying sophisticated econometric formulas and continuous statistical variance analyses within Lean Six Sigma in Enterprise Tech. Financial controllers monitor key performance thresholds in Value Stream Mapping for Slashing Digital Deployment Lead Times, mandating that operational throughput matches predefined benchmarks while defect rates remain strictly controlled. Embedding these quantitative benchmarks for Value Stream Mapping for Slashing Digital Deployment Lead Times into automated financial ledgers ensures that corporate capital allocations remain disciplined, defensible, and fully aligned with strategic corporate objectives.
Deploying structured operational workflows within Value Stream Mapping for Slashing Digital Deployment Lead Times requires configuring automated data telemetry and real-time monitoring across all functional Lean Six Sigma in Enterprise Tech touchpoints. For enterprise organizations seeking regulatory clarity regarding Value Stream Mapping for Slashing Digital Deployment Lead Times, referencing validated benchmarks published by institutional portals such as Apache Software Foundation architecture guidelines provides foundational compliance criteria that satisfy external regulatory authorities and institutional audit bodies. This automated operational telemetry layer for Value Stream Mapping for Slashing Digital Deployment Lead Times transforms reactive troubleshooting into proactive risk containment, ensuring continuous business continuity across high-pressure environments.
From a regulatory compliance perspective, managing Value Stream Mapping for Slashing Digital Deployment Lead Times requires strict adherence to statutory directives, regional licensing requirements, and industry-specific covenants governing Lean Six Sigma in Enterprise Tech. Corporate legal counsel must verify that all operational documentation regarding Value Stream Mapping for Slashing Digital Deployment Lead Times strictly aligns with statutory disclosure rules, mitigating the risk of administrative penalties or statutory enforcement inquiries. This rigorous statutory posture surrounding Value Stream Mapping for Slashing Digital Deployment Lead Times shields the enterprise against costly administrative proceedings, safeguarding institutional capital and protecting corporate leadership from personal liability.
Long-term institutional governance over Value Stream Mapping for Slashing Digital Deployment Lead Times demands structured board oversight, unannounced third-party compliance audits, and transparent executive scorecards across Lean Six Sigma in Enterprise Tech. Comprehensive audit trails and timestamped forensic logs for Value Stream Mapping for Slashing Digital Deployment Lead Times provide corporate leadership with verifiable legal evidence of proactive operational diligence, protecting executive directors against shareholder litigation. Ultimately, establishing these institutional governance protocols for Value Stream Mapping for Slashing Digital Deployment Lead Times guarantees that corporate operations remain structurally sound, commercially competitive, and fully compliant with statutory expectations.
Eliminating Waste (Muda) in Cloud Resource Overprovisioning
Establishing an institutional operating posture within Eliminating Waste (Muda) in Cloud Resource Overprovisioning requires enterprise leadership to deconstruct systemic dependencies across modern Lean Six Sigma in Enterprise Tech networks. Detailed analytical evaluations indicate that procedural deficiencies surrounding Eliminating Waste (Muda) in Cloud Resource Overprovisioning stem primarily from fragmented oversight mechanisms and delayed incident escalation protocols. Consequently, structuring a comprehensive operational defense around Eliminating Waste (Muda) in Cloud Resource Overprovisioning ensures that core institutional capabilities remain unimpaired throughout prolonged periods of commercial turbulence.
From a quantitative modeling standpoint, managing Eliminating Waste (Muda) in Cloud Resource Overprovisioning requires deploying sophisticated econometric formulas and continuous statistical variance analyses within Lean Six Sigma in Enterprise Tech. Financial controllers monitor key performance thresholds in Eliminating Waste (Muda) in Cloud Resource Overprovisioning, mandating that operational throughput matches predefined benchmarks while defect rates remain strictly controlled. Embedding these quantitative benchmarks for Eliminating Waste (Muda) in Cloud Resource Overprovisioning into automated financial ledgers ensures that corporate capital allocations remain disciplined, defensible, and fully aligned with strategic corporate objectives.
Deploying structured operational workflows within Eliminating Waste (Muda) in Cloud Resource Overprovisioning requires configuring automated data telemetry and real-time monitoring across all functional Lean Six Sigma in Enterprise Tech touchpoints. For enterprise organizations seeking regulatory clarity regarding Eliminating Waste (Muda) in Cloud Resource Overprovisioning, referencing validated benchmarks published by institutional portals such as Harvard Business Review operational excellence analyses provides foundational compliance criteria that satisfy external regulatory authorities and institutional audit bodies. This automated operational telemetry layer for Eliminating Waste (Muda) in Cloud Resource Overprovisioning transforms reactive troubleshooting into proactive risk containment, ensuring continuous business continuity across high-pressure environments.
From a regulatory compliance perspective, managing Eliminating Waste (Muda) in Cloud Resource Overprovisioning requires strict adherence to statutory directives, regional licensing requirements, and industry-specific covenants governing Lean Six Sigma in Enterprise Tech. Corporate legal counsel must verify that all operational documentation regarding Eliminating Waste (Muda) in Cloud Resource Overprovisioning strictly aligns with statutory disclosure rules, mitigating the risk of administrative penalties or statutory enforcement inquiries. This rigorous statutory posture surrounding Eliminating Waste (Muda) in Cloud Resource Overprovisioning shields the enterprise against costly administrative proceedings, safeguarding institutional capital and protecting corporate leadership from personal liability.
Long-term institutional governance over Eliminating Waste (Muda) in Cloud Resource Overprovisioning demands structured board oversight, unannounced third-party compliance audits, and transparent executive scorecards across Lean Six Sigma in Enterprise Tech. Comprehensive audit trails and timestamped forensic logs for Eliminating Waste (Muda) in Cloud Resource Overprovisioning provide corporate leadership with verifiable legal evidence of proactive operational diligence, protecting executive directors against shareholder litigation. Ultimately, establishing these institutional governance protocols for Eliminating Waste (Muda) in Cloud Resource Overprovisioning guarantees that corporate operations remain structurally sound, commercially competitive, and fully compliant with statutory expectations.
Statistical Process Control (SPC) for API Latency and Error Rates
Establishing an institutional operating posture within Statistical Process Control (SPC) for API Latency and Error Rates requires enterprise leadership to deconstruct systemic dependencies across modern Lean Six Sigma in Enterprise Tech networks. Detailed analytical evaluations indicate that procedural deficiencies surrounding Statistical Process Control (SPC) for API Latency and Error Rates stem primarily from fragmented oversight mechanisms and delayed incident escalation protocols. Consequently, structuring a comprehensive operational defense around Statistical Process Control (SPC) for API Latency and Error Rates ensures that core institutional capabilities remain unimpaired throughout prolonged periods of commercial turbulence.
From a quantitative modeling standpoint, managing Statistical Process Control (SPC) for API Latency and Error Rates requires deploying sophisticated econometric formulas and continuous statistical variance analyses within Lean Six Sigma in Enterprise Tech. Financial controllers monitor key performance thresholds in Statistical Process Control (SPC) for API Latency and Error Rates, mandating that operational throughput matches predefined benchmarks while defect rates remain strictly controlled. Embedding these quantitative benchmarks for Statistical Process Control (SPC) for API Latency and Error Rates into automated financial ledgers ensures that corporate capital allocations remain disciplined, defensible, and fully aligned with strategic corporate objectives.
Deploying structured operational workflows within Statistical Process Control (SPC) for API Latency and Error Rates requires configuring automated data telemetry and real-time monitoring across all functional Lean Six Sigma in Enterprise Tech touchpoints. When unexpected operational variances emerge within Statistical Process Control (SPC) for API Latency and Error Rates, automated telemetry triggers immediate alert notifications to dedicated incident response squads, initiating pre-approved remediation protocols within minutes of threshold detection. This automated operational telemetry layer for Statistical Process Control (SPC) for API Latency and Error Rates transforms reactive troubleshooting into proactive risk containment, ensuring continuous business continuity across high-pressure environments.
From a regulatory compliance perspective, managing Statistical Process Control (SPC) for API Latency and Error Rates requires strict adherence to statutory directives, regional licensing requirements, and industry-specific covenants governing Lean Six Sigma in Enterprise Tech. Corporate legal counsel must verify that all operational documentation regarding Statistical Process Control (SPC) for API Latency and Error Rates strictly aligns with statutory disclosure rules, mitigating the risk of administrative penalties or statutory enforcement inquiries. This rigorous statutory posture surrounding Statistical Process Control (SPC) for API Latency and Error Rates shields the enterprise against costly administrative proceedings, safeguarding institutional capital and protecting corporate leadership from personal liability.
Long-term institutional governance over Statistical Process Control (SPC) for API Latency and Error Rates demands structured board oversight, unannounced third-party compliance audits, and transparent executive scorecards across Lean Six Sigma in Enterprise Tech. Comprehensive audit trails and timestamped forensic logs for Statistical Process Control (SPC) for API Latency and Error Rates provide corporate leadership with verifiable legal evidence of proactive operational diligence, protecting executive directors against shareholder litigation. Ultimately, establishing these institutional governance protocols for Statistical Process Control (SPC) for API Latency and Error Rates guarantees that corporate operations remain structurally sound, commercially competitive, and fully compliant with statutory expectations.
Root Cause Analysis for Recurring System Outages and Bug Regressions
Establishing an institutional operating posture within Root Cause Analysis for Recurring System Outages and Bug Regressions requires enterprise leadership to deconstruct systemic dependencies across modern Lean Six Sigma in Enterprise Tech networks. Detailed analytical evaluations indicate that procedural deficiencies surrounding Root Cause Analysis for Recurring System Outages and Bug Regressions stem primarily from fragmented oversight mechanisms and delayed incident escalation protocols. Consequently, structuring a comprehensive operational defense around Root Cause Analysis for Recurring System Outages and Bug Regressions ensures that core institutional capabilities remain unimpaired throughout prolonged periods of commercial turbulence.
From a quantitative modeling standpoint, managing Root Cause Analysis for Recurring System Outages and Bug Regressions requires deploying sophisticated econometric formulas and continuous statistical variance analyses within Lean Six Sigma in Enterprise Tech. Financial controllers monitor key performance thresholds in Root Cause Analysis for Recurring System Outages and Bug Regressions, mandating that operational throughput matches predefined benchmarks while defect rates remain strictly controlled. Embedding these quantitative benchmarks for Root Cause Analysis for Recurring System Outages and Bug Regressions into automated financial ledgers ensures that corporate capital allocations remain disciplined, defensible, and fully aligned with strategic corporate objectives.
Deploying structured operational workflows within Root Cause Analysis for Recurring System Outages and Bug Regressions requires configuring automated data telemetry and real-time monitoring across all functional Lean Six Sigma in Enterprise Tech touchpoints. When unexpected operational variances emerge within Root Cause Analysis for Recurring System Outages and Bug Regressions, automated telemetry triggers immediate alert notifications to dedicated incident response squads, initiating pre-approved remediation protocols within minutes of threshold detection. This automated operational telemetry layer for Root Cause Analysis for Recurring System Outages and Bug Regressions transforms reactive troubleshooting into proactive risk containment, ensuring continuous business continuity across high-pressure environments.
From a regulatory compliance perspective, managing Root Cause Analysis for Recurring System Outages and Bug Regressions requires strict adherence to statutory directives, regional licensing requirements, and industry-specific covenants governing Lean Six Sigma in Enterprise Tech. Corporate legal counsel must verify that all operational documentation regarding Root Cause Analysis for Recurring System Outages and Bug Regressions strictly aligns with statutory disclosure rules, mitigating the risk of administrative penalties or statutory enforcement inquiries. This rigorous statutory posture surrounding Root Cause Analysis for Recurring System Outages and Bug Regressions shields the enterprise against costly administrative proceedings, safeguarding institutional capital and protecting corporate leadership from personal liability.
Long-term institutional governance over Root Cause Analysis for Recurring System Outages and Bug Regressions demands structured board oversight, unannounced third-party compliance audits, and transparent executive scorecards across Lean Six Sigma in Enterprise Tech. Comprehensive audit trails and timestamped forensic logs for Root Cause Analysis for Recurring System Outages and Bug Regressions provide corporate leadership with verifiable legal evidence of proactive operational diligence, protecting executive directors against shareholder litigation. Ultimately, establishing these institutional governance protocols for Root Cause Analysis for Recurring System Outages and Bug Regressions guarantees that corporate operations remain structurally sound, commercially competitive, and fully compliant with statutory expectations.
Standard Work Architecture in DevOps and Continuous Delivery Pipelines
Establishing an institutional operating posture within Standard Work Architecture in DevOps and Continuous Delivery Pipelines requires enterprise leadership to deconstruct systemic dependencies across modern Lean Six Sigma in Enterprise Tech networks. Detailed analytical evaluations indicate that procedural deficiencies surrounding Standard Work Architecture in DevOps and Continuous Delivery Pipelines stem primarily from fragmented oversight mechanisms and delayed incident escalation protocols. Consequently, structuring a comprehensive operational defense around Standard Work Architecture in DevOps and Continuous Delivery Pipelines ensures that core institutional capabilities remain unimpaired throughout prolonged periods of commercial turbulence.
From a quantitative modeling standpoint, managing Standard Work Architecture in DevOps and Continuous Delivery Pipelines requires deploying sophisticated econometric formulas and continuous statistical variance analyses within Lean Six Sigma in Enterprise Tech. Financial controllers monitor key performance thresholds in Standard Work Architecture in DevOps and Continuous Delivery Pipelines, mandating that operational throughput matches predefined benchmarks while defect rates remain strictly controlled. Embedding these quantitative benchmarks for Standard Work Architecture in DevOps and Continuous Delivery Pipelines into automated financial ledgers ensures that corporate capital allocations remain disciplined, defensible, and fully aligned with strategic corporate objectives.
Deploying structured operational workflows within Standard Work Architecture in DevOps and Continuous Delivery Pipelines requires configuring automated data telemetry and real-time monitoring across all functional Lean Six Sigma in Enterprise Tech touchpoints. When unexpected operational variances emerge within Standard Work Architecture in DevOps and Continuous Delivery Pipelines, automated telemetry triggers immediate alert notifications to dedicated incident response squads, initiating pre-approved remediation protocols within minutes of threshold detection. This automated operational telemetry layer for Standard Work Architecture in DevOps and Continuous Delivery Pipelines transforms reactive troubleshooting into proactive risk containment, ensuring continuous business continuity across high-pressure environments.
From a regulatory compliance perspective, managing Standard Work Architecture in DevOps and Continuous Delivery Pipelines requires strict adherence to statutory directives, regional licensing requirements, and industry-specific covenants governing Lean Six Sigma in Enterprise Tech. Corporate legal counsel must verify that all operational documentation regarding Standard Work Architecture in DevOps and Continuous Delivery Pipelines strictly aligns with statutory disclosure rules, mitigating the risk of administrative penalties or statutory enforcement inquiries. This rigorous statutory posture surrounding Standard Work Architecture in DevOps and Continuous Delivery Pipelines shields the enterprise against costly administrative proceedings, safeguarding institutional capital and protecting corporate leadership from personal liability.
Long-term institutional governance over Standard Work Architecture in DevOps and Continuous Delivery Pipelines demands structured board oversight, unannounced third-party compliance audits, and transparent executive scorecards across Lean Six Sigma in Enterprise Tech. Comprehensive audit trails and timestamped forensic logs for Standard Work Architecture in DevOps and Continuous Delivery Pipelines provide corporate leadership with verifiable legal evidence of proactive operational diligence, protecting executive directors against shareholder litigation. Ultimately, establishing these institutional governance protocols for Standard Work Architecture in DevOps and Continuous Delivery Pipelines guarantees that corporate operations remain structurally sound, commercially competitive, and fully compliant with statutory expectations.
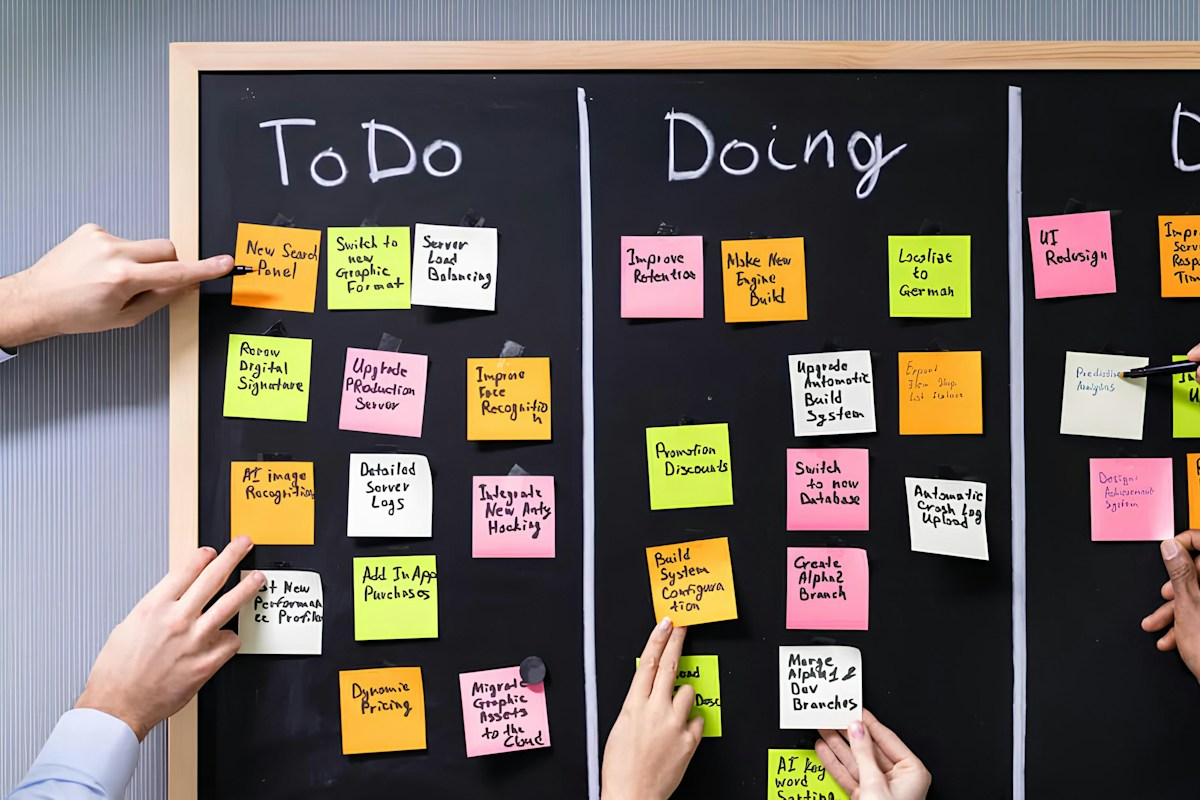
Kaizen Event Execution for Enterprise Software Refactoring
Establishing an institutional operating posture within Kaizen Event Execution for Enterprise Software Refactoring requires enterprise leadership to deconstruct systemic dependencies across modern Lean Six Sigma in Enterprise Tech networks. Detailed analytical evaluations indicate that procedural deficiencies surrounding Kaizen Event Execution for Enterprise Software Refactoring stem primarily from fragmented oversight mechanisms and delayed incident escalation protocols. Consequently, structuring a comprehensive operational defense around Kaizen Event Execution for Enterprise Software Refactoring ensures that core institutional capabilities remain unimpaired throughout prolonged periods of commercial turbulence.
From a quantitative modeling standpoint, managing Kaizen Event Execution for Enterprise Software Refactoring requires deploying sophisticated econometric formulas and continuous statistical variance analyses within Lean Six Sigma in Enterprise Tech. Financial controllers monitor key performance thresholds in Kaizen Event Execution for Enterprise Software Refactoring, mandating that operational throughput matches predefined benchmarks while defect rates remain strictly controlled. Embedding these quantitative benchmarks for Kaizen Event Execution for Enterprise Software Refactoring into automated financial ledgers ensures that corporate capital allocations remain disciplined, defensible, and fully aligned with strategic corporate objectives.
Deploying structured operational workflows within Kaizen Event Execution for Enterprise Software Refactoring requires configuring automated data telemetry and real-time monitoring across all functional Lean Six Sigma in Enterprise Tech touchpoints. When unexpected operational variances emerge within Kaizen Event Execution for Enterprise Software Refactoring, automated telemetry triggers immediate alert notifications to dedicated incident response squads, initiating pre-approved remediation protocols within minutes of threshold detection. This automated operational telemetry layer for Kaizen Event Execution for Enterprise Software Refactoring transforms reactive troubleshooting into proactive risk containment, ensuring continuous business continuity across high-pressure environments.
From a regulatory compliance perspective, managing Kaizen Event Execution for Enterprise Software Refactoring requires strict adherence to statutory directives, regional licensing requirements, and industry-specific covenants governing Lean Six Sigma in Enterprise Tech. Corporate legal counsel must verify that all operational documentation regarding Kaizen Event Execution for Enterprise Software Refactoring strictly aligns with statutory disclosure rules, mitigating the risk of administrative penalties or statutory enforcement inquiries. This rigorous statutory posture surrounding Kaizen Event Execution for Enterprise Software Refactoring shields the enterprise against costly administrative proceedings, safeguarding institutional capital and protecting corporate leadership from personal liability.
Long-term institutional governance over Kaizen Event Execution for Enterprise Software Refactoring demands structured board oversight, unannounced third-party compliance audits, and transparent executive scorecards across Lean Six Sigma in Enterprise Tech. Comprehensive audit trails and timestamped forensic logs for Kaizen Event Execution for Enterprise Software Refactoring provide corporate leadership with verifiable legal evidence of proactive operational diligence, protecting executive directors against shareholder litigation. Ultimately, establishing these institutional governance protocols for Kaizen Event Execution for Enterprise Software Refactoring guarantees that corporate operations remain structurally sound, commercially competitive, and fully compliant with statutory expectations.
Balancing Agile Velocity with Six Sigma Defect Elimination Rigor
Establishing an institutional operating posture within Balancing Agile Velocity with Six Sigma Defect Elimination Rigor requires enterprise leadership to deconstruct systemic dependencies across modern Lean Six Sigma in Enterprise Tech networks. Detailed analytical evaluations indicate that procedural deficiencies surrounding Balancing Agile Velocity with Six Sigma Defect Elimination Rigor stem primarily from fragmented oversight mechanisms and delayed incident escalation protocols. Consequently, structuring a comprehensive operational defense around Balancing Agile Velocity with Six Sigma Defect Elimination Rigor ensures that core institutional capabilities remain unimpaired throughout prolonged periods of commercial turbulence.
From a quantitative modeling standpoint, managing Balancing Agile Velocity with Six Sigma Defect Elimination Rigor requires deploying sophisticated econometric formulas and continuous statistical variance analyses within Lean Six Sigma in Enterprise Tech. Financial controllers monitor key performance thresholds in Balancing Agile Velocity with Six Sigma Defect Elimination Rigor, mandating that operational throughput matches predefined benchmarks while defect rates remain strictly controlled. Embedding these quantitative benchmarks for Balancing Agile Velocity with Six Sigma Defect Elimination Rigor into automated financial ledgers ensures that corporate capital allocations remain disciplined, defensible, and fully aligned with strategic corporate objectives.
Deploying structured operational workflows within Balancing Agile Velocity with Six Sigma Defect Elimination Rigor requires configuring automated data telemetry and real-time monitoring across all functional Lean Six Sigma in Enterprise Tech touchpoints. When unexpected operational variances emerge within Balancing Agile Velocity with Six Sigma Defect Elimination Rigor, automated telemetry triggers immediate alert notifications to dedicated incident response squads, initiating pre-approved remediation protocols within minutes of threshold detection. This automated operational telemetry layer for Balancing Agile Velocity with Six Sigma Defect Elimination Rigor transforms reactive troubleshooting into proactive risk containment, ensuring continuous business continuity across high-pressure environments.
From a regulatory compliance perspective, managing Balancing Agile Velocity with Six Sigma Defect Elimination Rigor requires strict adherence to statutory directives, regional licensing requirements, and industry-specific covenants governing Lean Six Sigma in Enterprise Tech. Corporate legal counsel must verify that all operational documentation regarding Balancing Agile Velocity with Six Sigma Defect Elimination Rigor strictly aligns with statutory disclosure rules, mitigating the risk of administrative penalties or statutory enforcement inquiries. This rigorous statutory posture surrounding Balancing Agile Velocity with Six Sigma Defect Elimination Rigor shields the enterprise against costly administrative proceedings, safeguarding institutional capital and protecting corporate leadership from personal liability.
Long-term institutional governance over Balancing Agile Velocity with Six Sigma Defect Elimination Rigor demands structured board oversight, unannounced third-party compliance audits, and transparent executive scorecards across Lean Six Sigma in Enterprise Tech. Comprehensive audit trails and timestamped forensic logs for Balancing Agile Velocity with Six Sigma Defect Elimination Rigor provide corporate leadership with verifiable legal evidence of proactive operational diligence, protecting executive directors against shareholder litigation. Ultimately, establishing these institutional governance protocols for Balancing Agile Velocity with Six Sigma Defect Elimination Rigor guarantees that corporate operations remain structurally sound, commercially competitive, and fully compliant with statutory expectations.
Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems
Establishing an institutional operating posture within Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems requires enterprise leadership to deconstruct systemic dependencies across modern Lean Six Sigma in Enterprise Tech networks. Detailed analytical evaluations indicate that procedural deficiencies surrounding Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems stem primarily from fragmented oversight mechanisms and delayed incident escalation protocols. Consequently, structuring a comprehensive operational defense around Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems ensures that core institutional capabilities remain unimpaired throughout prolonged periods of commercial turbulence.
From a quantitative modeling standpoint, managing Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems requires deploying sophisticated econometric formulas and continuous statistical variance analyses within Lean Six Sigma in Enterprise Tech. Financial controllers monitor key performance thresholds in Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems, mandating that operational throughput matches predefined benchmarks while defect rates remain strictly controlled. Embedding these quantitative benchmarks for Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems into automated financial ledgers ensures that corporate capital allocations remain disciplined, defensible, and fully aligned with strategic corporate objectives.
Deploying structured operational workflows within Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems requires configuring automated data telemetry and real-time monitoring across all functional Lean Six Sigma in Enterprise Tech touchpoints. When unexpected operational variances emerge within Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems, automated telemetry triggers immediate alert notifications to dedicated incident response squads, initiating pre-approved remediation protocols within minutes of threshold detection. This automated operational telemetry layer for Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems transforms reactive troubleshooting into proactive risk containment, ensuring continuous business continuity across high-pressure environments.
From a regulatory compliance perspective, managing Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems requires strict adherence to statutory directives, regional licensing requirements, and industry-specific covenants governing Lean Six Sigma in Enterprise Tech. Corporate legal counsel must verify that all operational documentation regarding Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems strictly aligns with statutory disclosure rules, mitigating the risk of administrative penalties or statutory enforcement inquiries. This rigorous statutory posture surrounding Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems shields the enterprise against costly administrative proceedings, safeguarding institutional capital and protecting corporate leadership from personal liability.
Long-term institutional governance over Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems demands structured board oversight, unannounced third-party compliance audits, and transparent executive scorecards across Lean Six Sigma in Enterprise Tech. Comprehensive audit trails and timestamped forensic logs for Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems provide corporate leadership with verifiable legal evidence of proactive operational diligence, protecting executive directors against shareholder litigation. Ultimately, establishing these institutional governance protocols for Measuring Cost of Poor Quality (COPQ) in Digital Enterprise Systems guarantees that corporate operations remain structurally sound, commercially competitive, and fully compliant with statutory expectations.
Cultural Transformation and Black Belt Leadership in Engineering Teams
Establishing an institutional operating posture within Cultural Transformation and Black Belt Leadership in Engineering Teams requires enterprise leadership to deconstruct systemic dependencies across modern Lean Six Sigma in Enterprise Tech networks. Detailed analytical evaluations indicate that procedural deficiencies surrounding Cultural Transformation and Black Belt Leadership in Engineering Teams stem primarily from fragmented oversight mechanisms and delayed incident escalation protocols. Consequently, structuring a comprehensive operational defense around Cultural Transformation and Black Belt Leadership in Engineering Teams ensures that core institutional capabilities remain unimpaired throughout prolonged periods of commercial turbulence.
From a quantitative modeling standpoint, managing Cultural Transformation and Black Belt Leadership in Engineering Teams requires deploying sophisticated econometric formulas and continuous statistical variance analyses within Lean Six Sigma in Enterprise Tech. Financial controllers monitor key performance thresholds in Cultural Transformation and Black Belt Leadership in Engineering Teams, mandating that operational throughput matches predefined benchmarks while defect rates remain strictly controlled. Embedding these quantitative benchmarks for Cultural Transformation and Black Belt Leadership in Engineering Teams into automated financial ledgers ensures that corporate capital allocations remain disciplined, defensible, and fully aligned with strategic corporate objectives.
Deploying structured operational workflows within Cultural Transformation and Black Belt Leadership in Engineering Teams requires configuring automated data telemetry and real-time monitoring across all functional Lean Six Sigma in Enterprise Tech touchpoints. When unexpected operational variances emerge within Cultural Transformation and Black Belt Leadership in Engineering Teams, automated telemetry triggers immediate alert notifications to dedicated incident response squads, initiating pre-approved remediation protocols within minutes of threshold detection. This automated operational telemetry layer for Cultural Transformation and Black Belt Leadership in Engineering Teams transforms reactive troubleshooting into proactive risk containment, ensuring continuous business continuity across high-pressure environments.
From a regulatory compliance perspective, managing Cultural Transformation and Black Belt Leadership in Engineering Teams requires strict adherence to statutory directives, regional licensing requirements, and industry-specific covenants governing Lean Six Sigma in Enterprise Tech. Corporate legal counsel must verify that all operational documentation regarding Cultural Transformation and Black Belt Leadership in Engineering Teams strictly aligns with statutory disclosure rules, mitigating the risk of administrative penalties or statutory enforcement inquiries. This rigorous statutory posture surrounding Cultural Transformation and Black Belt Leadership in Engineering Teams shields the enterprise against costly administrative proceedings, safeguarding institutional capital and protecting corporate leadership from personal liability.
Long-term institutional governance over Cultural Transformation and Black Belt Leadership in Engineering Teams demands structured board oversight, unannounced third-party compliance audits, and transparent executive scorecards across Lean Six Sigma in Enterprise Tech. Comprehensive audit trails and timestamped forensic logs for Cultural Transformation and Black Belt Leadership in Engineering Teams provide corporate leadership with verifiable legal evidence of proactive operational diligence, protecting executive directors against shareholder litigation. Ultimately, establishing these institutional governance protocols for Cultural Transformation and Black Belt Leadership in Engineering Teams guarantees that corporate operations remain structurally sound, commercially competitive, and fully compliant with statutory expectations.
Executive Dashboard Design for Operational Process Excellence
Establishing an institutional operating posture within Executive Dashboard Design for Operational Process Excellence requires enterprise leadership to deconstruct systemic dependencies across modern Lean Six Sigma in Enterprise Tech networks. Detailed analytical evaluations indicate that procedural deficiencies surrounding Executive Dashboard Design for Operational Process Excellence stem primarily from fragmented oversight mechanisms and delayed incident escalation protocols. Consequently, structuring a comprehensive operational defense around Executive Dashboard Design for Operational Process Excellence ensures that core institutional capabilities remain unimpaired throughout prolonged periods of commercial turbulence.
From a quantitative modeling standpoint, managing Executive Dashboard Design for Operational Process Excellence requires deploying sophisticated econometric formulas and continuous statistical variance analyses within Lean Six Sigma in Enterprise Tech. Financial controllers monitor key performance thresholds in Executive Dashboard Design for Operational Process Excellence, mandating that operational throughput matches predefined benchmarks while defect rates remain strictly controlled. Embedding these quantitative benchmarks for Executive Dashboard Design for Operational Process Excellence into automated financial ledgers ensures that corporate capital allocations remain disciplined, defensible, and fully aligned with strategic corporate objectives.
Deploying structured operational workflows within Executive Dashboard Design for Operational Process Excellence requires configuring automated data telemetry and real-time monitoring across all functional Lean Six Sigma in Enterprise Tech touchpoints. When unexpected operational variances emerge within Executive Dashboard Design for Operational Process Excellence, automated telemetry triggers immediate alert notifications to dedicated incident response squads, initiating pre-approved remediation protocols within minutes of threshold detection. This automated operational telemetry layer for Executive Dashboard Design for Operational Process Excellence transforms reactive troubleshooting into proactive risk containment, ensuring continuous business continuity across high-pressure environments.
From a regulatory compliance perspective, managing Executive Dashboard Design for Operational Process Excellence requires strict adherence to statutory directives, regional licensing requirements, and industry-specific covenants governing Lean Six Sigma in Enterprise Tech. Corporate legal counsel must verify that all operational documentation regarding Executive Dashboard Design for Operational Process Excellence strictly aligns with statutory disclosure rules, mitigating the risk of administrative penalties or statutory enforcement inquiries. This rigorous statutory posture surrounding Executive Dashboard Design for Operational Process Excellence shields the enterprise against costly administrative proceedings, safeguarding institutional capital and protecting corporate leadership from personal liability.
Long-term institutional governance over Executive Dashboard Design for Operational Process Excellence demands structured board oversight, unannounced third-party compliance audits, and transparent executive scorecards across Lean Six Sigma in Enterprise Tech. Comprehensive audit trails and timestamped forensic logs for Executive Dashboard Design for Operational Process Excellence provide corporate leadership with verifiable legal evidence of proactive operational diligence, protecting executive directors against shareholder litigation. Ultimately, establishing these institutional governance protocols for Executive Dashboard Design for Operational Process Excellence guarantees that corporate operations remain structurally sound, commercially competitive, and fully compliant with statutory expectations.
Comprehensive Strategic Roadmap for Institutional Process Mastery
Establishing an institutional operating posture within Comprehensive Strategic Roadmap for Institutional Process Mastery requires enterprise leadership to deconstruct systemic dependencies across modern Lean Six Sigma in Enterprise Tech networks. Detailed analytical evaluations indicate that procedural deficiencies surrounding Comprehensive Strategic Roadmap for Institutional Process Mastery stem primarily from fragmented oversight mechanisms and delayed incident escalation protocols. Consequently, structuring a comprehensive operational defense around Comprehensive Strategic Roadmap for Institutional Process Mastery ensures that core institutional capabilities remain unimpaired throughout prolonged periods of commercial turbulence.
From a quantitative modeling standpoint, managing Comprehensive Strategic Roadmap for Institutional Process Mastery requires deploying sophisticated econometric formulas and continuous statistical variance analyses within Lean Six Sigma in Enterprise Tech. Financial controllers monitor key performance thresholds in Comprehensive Strategic Roadmap for Institutional Process Mastery, mandating that operational throughput matches predefined benchmarks while defect rates remain strictly controlled. Embedding these quantitative benchmarks for Comprehensive Strategic Roadmap for Institutional Process Mastery into automated financial ledgers ensures that corporate capital allocations remain disciplined, defensible, and fully aligned with strategic corporate objectives.
Deploying structured operational workflows within Comprehensive Strategic Roadmap for Institutional Process Mastery requires configuring automated data telemetry and real-time monitoring across all functional Lean Six Sigma in Enterprise Tech touchpoints. When unexpected operational variances emerge within Comprehensive Strategic Roadmap for Institutional Process Mastery, automated telemetry triggers immediate alert notifications to dedicated incident response squads, initiating pre-approved remediation protocols within minutes of threshold detection. This automated operational telemetry layer for Comprehensive Strategic Roadmap for Institutional Process Mastery transforms reactive troubleshooting into proactive risk containment, ensuring continuous business continuity across high-pressure environments.
From a regulatory compliance perspective, managing Comprehensive Strategic Roadmap for Institutional Process Mastery requires strict adherence to statutory directives, regional licensing requirements, and industry-specific covenants governing Lean Six Sigma in Enterprise Tech. Corporate legal counsel must verify that all operational documentation regarding Comprehensive Strategic Roadmap for Institutional Process Mastery strictly aligns with statutory disclosure rules, mitigating the risk of administrative penalties or statutory enforcement inquiries. This rigorous statutory posture surrounding Comprehensive Strategic Roadmap for Institutional Process Mastery shields the enterprise against costly administrative proceedings, safeguarding institutional capital and protecting corporate leadership from personal liability.
Long-term institutional governance over Comprehensive Strategic Roadmap for Institutional Process Mastery demands structured board oversight, unannounced third-party compliance audits, and transparent executive scorecards across Lean Six Sigma in Enterprise Tech. Comprehensive audit trails and timestamped forensic logs for Comprehensive Strategic Roadmap for Institutional Process Mastery provide corporate leadership with verifiable legal evidence of proactive operational diligence, protecting executive directors against shareholder litigation. Ultimately, establishing these institutional governance protocols for Comprehensive Strategic Roadmap for Institutional Process Mastery guarantees that corporate operations remain structurally sound, commercially competitive, and fully compliant with statutory expectations.
Comparative Institutional Implementation and Risk Governance Matrix
To provide executive leadership with a structured operational overview, the following diagnostic matrix contrasts primary implementation dimensions within Lean Six Sigma in Enterprise Tech against corresponding technical standards, common vulnerability vectors, and target operational KPIs:
| Governance Dimension | Primary Vulnerability Vector | Core Technical Mitigation Protocol | Target Operational KPI |
|---|---|---|---|
| Defect Rate Reduction | Production deployment defects causing client-facing application outages | DMAIC framework with automated unit test coverage and static code analysis | Defect density reduced below 0.15 defects per 1,000 lines of executable code |
| Pipeline Cycle Time | Prolonged build and testing queues delaying software release cycles | Value stream mapping of CI/CD pipelines and parallel containerized testing | Deployment cycle time compressed from 14 days to sub-2-hour automated releases |
| Root-Cause Analysis | Recurring recurring system regressions due to superficial incident patching | 5-Whys and Ishikawa fishbone analysis integrated into post-mortem workflows | Zero repeat software regressions across quarterly production release cycles |
| Statistical Process Control | Unmonitored variance in API response latency across cloud clusters | Shewhart control charts and automated latency variance alerting in APM consoles | 99.9th percentile API latency maintained strictly within 3 sigma control limits |
| Engineering Waste (Muda) | Developer idle time waiting for manual QA approvals and code reviews | Continuous testing automation and automated pull request dependency bots | Developer productive time increased by 28%, eliminating staging test bottlenecks |
| Customer Value Delivery | Feature bloat delivering complex tools that end-users rarely utilize | Voice of the Customer (VoC) analytics and telemetry-driven feature flagging | Feature adoption rate increased to 82% within 30 days of production rollout |
By systematically reviewing and implementing the standards outlined in this matrix, corporate leadership teams establish clear operational accountability, streamline multi-departmental workflows, and build an institutional buffer against unexpected macroeconomic and technical dislocations in Lean Six Sigma in Enterprise Tech.
Frequently Asked Questions About Lean Six Sigma in Enterprise Tech
How does Lean Six Sigma DMAIC apply to modern agile software development?
DMAIC (Define, Measure, Analyze, Improve, Control) provides a structured statistical framework to identify software pipeline bottlenecks, measure defect rates, and sustain process improvements.
What is Value Stream Mapping in enterprise software engineering?
Value Stream Mapping visually documents every step required to take code from commit to production, exposing idle queues, manual handoffs, and unnecessary verification delays.
How do Shewhart control charts detect performance regressions in cloud architectures?
Control charts establish upper and lower statistical bounds on API latency and server load, alerting engineers when latency exceeds normal operational variance before failure occurs.
What constitutes ‘waste’ (Muda) in digital engineering workflows?
Waste includes manual environment provisioning, context-switching between fragmented tools, redundant documentation, waiting on code reviews, and building unvalidated features.
How does Six Sigma defect density measurement compare to traditional software QA?
Traditional QA measures bug counts, whereas Six Sigma calculates Defects Per Million Opportunities (DPMO), enabling standardized statistical benchmarking across diverse codebases.
What role do automated CI/CD automated gates play in Six Sigma error prevention (Poka-Yoke)?
Automated deployment gates block code promotion if automated unit tests, linting, or security vulnerability scans fail, mechanically preventing defects from reaching production.
How does Voice of the Customer (VoC) telemetry guide product engineering priorities?
In-app analytics track actual feature engagement, drop-off rates, and user friction, ensuring engineering CapEx is allocated exclusively to features that drive customer retention.
How frequently should software engineering teams conduct Lean Kaizen events?
Engineering departments should conduct quarterly targeted Kaizen sprints focusing on specific systemic friction points, such as flaky test suites or database migration delays.
Strategic Five-Year Operational Roadmap for Institutional Leaders
Navigating volatile commercial environments across Enterprise Software Engineering and Lean Six Sigma Deployment requires enterprise executives to transform Lean Six Sigma in Enterprise Tech from a passive compliance exercise into an active operational strategy. The structural disruptions observed across modern regulatory frameworks, digital infrastructures, and competitive markets in Enterprise Software Engineering and Lean Six Sigma Deployment are permanent features of modern commerce. Organizations that invest in robust governance architectures, automated telemetry platforms, and disciplined risk-shifting firewalls for Lean Six Sigma in Enterprise Tech successfully insulate their balance sheets from external volatility.
Over the next five operating cycles, institutional leadership in Enterprise Software Engineering and Lean Six Sigma Deployment must commit capital toward modernizing core operational infrastructure for Lean Six Sigma in Enterprise Tech. By enforcing disciplined counterparty solvency reviews, establishing contractual firewalls, and integrating predictive analytics into daily workflows, enterprises ensure that operational hiccups in Lean Six Sigma in Enterprise Tech never threaten corporate solvency. These proactive investments across Enterprise Software Engineering and Lean Six Sigma Deployment solidify organizational resilience, enhance stakeholder trust, and guarantee sustained commercial leadership.
Ultimately, long-term commercial success in Enterprise Software Engineering and Lean Six Sigma Deployment belongs to enterprises that combine strategic foresight with rigorous technical execution in Lean Six Sigma in Enterprise Tech. Establishing comprehensive risk mitigation frameworks for Lean Six Sigma in Enterprise Tech preserves hard-won corporate value and positions forward-thinking organizations to capitalize on commercial opportunities while less resilient competitors struggle with operational disruptions.

